bookmark_borderHuge Credit Agency Data Breach

by Daniel Brouse and Sidd Mukherjee for Membrane Domain Security

Equifax is one of the largest credit reporting agencies in the world. Ironically, Equifax provides “identity protection tools with daily monitoring and alerts today!”

From May to July, 2017, Equifax allowed a cybersecurity breach to steal 143 million people’s identity. The stolen information includes social security numbers, birthdays, addresses and driver’s license numbers.

On September 7, Equifax released a statement via Twitter: “We recently discovered a cybersecurity incident involving consumer information. Once discovered, we acted immediately to stop the intrusion. We apologize to our consumers and business customers for the concern and frustration this causes. Learn more: .”

The data breach compromised about half the population of the United States.

Cyber security specialist Sidd Mukherjee said, “The main issue not addressed is the collection of the data in the first place. There would be no target if there were no centralized database. If the data were maintained in a distributed mechanism, with strict privacy guarantees and guaranteed update (such as blockchain/bittorent/tor allows) we would not be in this situation.

‘But that’s so hard and we need to make money this quarter’

OK, that is actually quite a cruel summary, so let me expand. Back in the day, centralized was the only way to go. The Internet made a lot of things possible and mathematics did as much. Companies like Equifax began in response to a need. They
glommed on to a need twenty years before the Internet and made big databases because they watched ATT and SABRE and railroads, and such. The Internet came along and they lumbered over. And now, they find they are in a strange and terrible land beset with pitfall and with snare.

Equifax makes money through collection and controlled distribution of data. Both those avenues and control are threatened in this brave new world, as Mr. Assange pointed out some time ago.

Don’t get me wrong. I actually think assaults on privacy have done the evolution thing, selected for those schemes which resist assault. And as such, the centralized databases will get selected out of the game. It will take a while, though.”

In other news, until you had many to many communication with latency lower than human attention span, which seems to be about 20 seconds, you can’t really do hive intelligence like the kids are doing with the cell phones. Watch the kids. Demographic is destiny, as someone said.”

bookmark_borderNSA Hack Set Loose on World

by Daniel Brouse for The Membrane Doamin

It appears that malware hacked from the NSA in April 2017 has been set loose on the world. The massive ransomware infection hit at least 99 countries. The ransomware is called WannaCry. The source was leaked as part of the NSA spytools. The code was modified by hackers to takeover computers. Then, a ransom note says you must pay $300 in BitCoin to save your computer. The price increases every couple of hours if the ransom isn’t paid. The ransomware spreads by taking advantage of a vulnerability in Microsoft Windows. Microsoft issued a patch after the NSA leak; however, computers that did not apply the patch were at risk.

In the UK, 16 National Health Service organizations were taken off-line. Europol said the attack was of an “unprecedented level and requires international investigation.” Cybersecurity firm Avast said, “the majority of the attacks targeted Russia, Ukraine and Taiwan. But U.K. hospitals, Chinese universities and global firms like Fedex also reported they had come under assault.”

Later in the day, the “accidental hero” halted the global spread. The Guardian reported, “The researcher, who identified himself only as MalwareTech, is a 22-year-old from south-west England who lives with his parents and works for Kryptos logic, an LA-based threat intelligence company.”

“I was out having lunch with a friend and got back about 3pm and saw an influx of news articles about the NHS and various UK organizations being hit,” he said. “I had a bit of a look into that and then I found a sample of the malware behind it, and saw that it was connecting out to a specific domain, which was not registered. So I picked it up not knowing what it did at the time.”

The fake domain name was a “kill switch” in the malware. When the domain really showed up on the Internet, the virus stopped replicating. “The intent was to just monitor the spread and see if we could do anything about it later on. But we actually stopped the spread just by registering the domain,” he said. “This is not over. The attackers will realize how we stopped it, they’ll change the code and then they’ll start again. Enable windows update, update and then reboot.”

At the writing of this article it is estimated that 1/2 million pounds have already been paid in ransom.

bookmark_borderVPN: Virtual Private Network and Internet Privacy

by Daniel Brouse and Sidd Mukherjee

Your Internet service provider (ISP) knows where you live, your address and billing info. They also know:

  • all the IPs and domain names you visit and when
  • all the content of your unencrypted traffic in and out, as well as, the timing

The federal government now allows your ISP to sell the information.

VPN: Virtual Private Network
VPN stands for virtual private network. A VPN builds an encrypted connection from your computer to your VPN provider and routes all your traffic through it. All your traffic now appears on the net through the IP of your VPN provider.

If you use a VPN, the only thing others can see is you making an encrypted connection to one IP that relays your traffic. If that IP is at the same location as you, you are still subject to a geolocation threat.

In addition to using a VPN, the following is recommended:

TURN OFF Cookies And Java
The easiest way to start protecting your privacy is turning off cookies and java in your browser. Cookies allow remote servers access to your internet activities. Your browser history is also subject to privacy violations. Only allow access to your cookies and browser history when you are confident of the websites you visit. If a site forces you to use cookies, clear your cookies and browser history after each visit.

Java and Java script allow remote servers to run programs on your computer. Java script is how most malware is downloaded onto your computer. Avoid Java at all costs.

AdBlock – Chrome
Advertisement blocking software can be added to most web browsers. AdBlock for Google’s Chrome is one of the highest rated. Google says, “AdBlock. The #1 ad blocker with over 200 million downloads. Blocks YouTube, Facebook and ads everywhere else on the web. The original AdBlock for Chrome works automatically. Choose to continue seeing unobtrusive ads, whitelist your favorite sites, or block all ads by default. Just click “Add to Chrome,” then visit your favorite website and see the ads disappear!”

IP Anonymizer
Protecting the privacy of your unique IP is the most important aspect of protecting your privacy. It is also fairly difficult. A VPN does not conceal your IP on the Internet.

The easiest and cheapest way to conceal your identity is with an IP Anonymizer. “This anonymizer will hide your IP address from the websites you access as well as protect you from tracking with cookies and other means.”

You can go to a site, such as, http://webanonymizer.org/ and enter the website you want to visit. WebAnonymizer will automatically mask your IP for free.

TOR
A Tor browser is free software for enabling anonymous communication. The Tor name is an acronym for the original software project name “The Onion Router”. Tor routes Internet traffic through a free, worldwide, volunteer network of more than seven thousand relays. A users location and usage is concealed from anyone conducting network surveillance or traffic analysis. Tor makes it very difficult for Internet activity to be traced including “visits to Web sites, online posts, instant messages, and other communication forms”.

The Tor project states, “The Tor software protects you by bouncing your communications around a distributed network of relays run by volunteers all around the world: it prevents somebody watching your Internet connection from learning what sites you visit, it prevents the sites you visit from learning your physical location, and it lets you access sites which are blocked. Tor Browser lets you use Tor on Windows, Mac OS X, or Linux without needing to install any software. It can run off a USB flash drive, comes with a pre-configured web browser to protect your anonymity, and is self-contained (portable).”

Download the Tor browser (free)

Comments
A reader asked: So is there still a place for a VPN on our mobile devices? When using public wifi for example?
A: Yes. Almost all public wifi’s are a private network. You just have to worry about the other people who are on the private network with you. A device on the private network is easily hacked by someone in close proximity (e.g. hackers can use a Pringles can as an antenna and gain access within several hundred yards http://www.lifehack.org/articles/lifehack/extend-your-wifi-range-using-diy-antenna-from-pringles-can.html)

From The Membrane Domain’s Cybersecurity Center

bookmark_borderRussia Hacked 500 Million Yahoo Accounts

The Membrane Domain: Cybersecurity

by the Department of Justice
Office of Public Affairs

A grand jury in the Northern District of California has indicted four defendants, including two officers of the Russian Federal Security Service (FSB), for computer hacking, economic espionage and other criminal offenses in connection with a conspiracy, beginning in January 2014, to access Yahoo’s network and the contents of webmail accounts. The defendants are Dmitry Aleksandrovich Dokuchaev, 33, a Russian national and resident; Igor Anatolyevich Sushchin, 43, a Russian national and resident; Alexsey Alexseyevich Belan, aka “Magg,” 29, a Russian national and resident; and Karim Baratov, aka “Kay,” “Karim Taloverov” and “Karim Akehmet Tokbergenov,” 22, a Canadian and Kazakh national and a resident of Canada.

The defendants used unauthorized access to Yahoo’s systems to steal information from about at least 500 million Yahoo accounts and then used some of that stolen information to obtain unauthorized access to the contents of accounts at Yahoo, Google and other webmail providers, including accounts of Russian journalists, U.S. and Russian government officials and private-sector employees of financial, transportation and other companies. One of the defendants also exploited his access to Yahoo’s network for his personal financial gain, by searching Yahoo user communications for credit card and gift card account numbers, redirecting a subset of Yahoo search engine web traffic so he could make commissions and enabling the theft of the contacts of at least 30 million Yahoo accounts to facilitate a spam campaign.

The charges were announced by Attorney General Jeff Sessions of the U.S. Department of Justice, Director James Comey of the FBI, Acting Assistant Attorney General Mary McCord of the National Security Division, U.S. Attorney Brian Stretch for the Northern District of California and Executive Assistant Director Paul Abbate of the FBI’s Criminal, Cyber, Response and Services Branch.

“Cyber crime poses a significant threat to our nation’s security and prosperity, and this is one of the largest data breaches in history,” said Attorney General Sessions. “But thanks to the tireless efforts of U.S. prosecutors and investigators, as well as our Canadian partners, today we have identified four individuals, including two Russian FSB officers, responsible for unauthorized access to millions of users’ accounts. The United States will vigorously investigate and prosecute the people behind such attacks to the fullest extent of the law.”

“Today we continue to pierce the veil of anonymity surrounding cyber crimes,” said Director Comey. “We are shrinking the world to ensure that cyber criminals think twice before targeting U.S. persons and interests.”

“ The criminal conduct at issue, carried out and otherwise facilitated by officers from an FSB unit that serves as the FBI’s point of contact in Moscow on cybercrime matters, is beyond the pale,” said Acting Assistant Attorney General McCord. “Once again, the Department and the FBI have demonstrated that hackers around the world can and will be exposed and held accountable. State actors may be using common criminals to access the data they want, but the indictment shows that our companies do not have to stand alone against this threat. We commend Yahoo and Google for their sustained and invaluable cooperation in the investigation aimed at obtaining justice for, and protecting the privacy of their users.”

“This is a highly complicated investigation of a very complex threat. It underscores the value of early, proactive engagement and cooperation between the private sector and the government,” said Executive Assistant Director Abbate. “The FBI will continue to work relentlessly with our private sector and international partners to identify those who conduct cyber-attacks against our citizens and our nation, expose them and hold them accountable under the law, no matter where they attempt to hide.”

“Silicon Valley’s computer infrastructure provides the means by which people around the world communicate with each other in their business and personal lives. The privacy and security of those communications must be governed by the rule of law, not by the whim of criminal hackers and those who employ them. People rightly expect that their communications through Silicon Valley internet providers will remain private, unless lawful authority provides otherwise. We will not tolerate unauthorized and illegal intrusions into the Silicon Valley computer infrastructure upon which both private citizens and the global economy rely,” said U.S. Attorney Stretch. “Working closely with Yahoo and Google, Department of Justice lawyers and the FBI were able to identify and expose the hackers responsible for the conduct described today, without unduly intruding into the privacy of the accounts that were stolen. We commend Yahoo and Google for providing exemplary cooperation while zealously protecting their users’ privacy.”

Summary of Allegations

According to the allegations of the Indictment:

The FSB officer defendants, Dmitry Dokuchaev and Igor Sushchin, protected, directed, facilitated and paid criminal hackers to collect information through computer intrusions in the U.S. and elsewhere. In the present case, they worked with co-defendants Alexsey Belan and Karim Baratov to obtain access to the email accounts of thousands of individuals.

Belan had been publicly indicted in September 2012 and June 2013 and was named one of FBI’s Cyber Most Wanted criminals in November 2013. An Interpol Red Notice seeking his immediate detention has been lodged (including with Russia) since July 26, 2013. Belan was arrested in a European country on a request from the U.S. in June 2013, but he was able to escape to Russia before he could be extradited.

Instead of acting on the U.S. government’s Red Notice and detaining Belan after his return, Dokuchaev and Sushchin subsequently used him to gain unauthorized access to Yahoo’s network. In or around November and December 2014, Belan stole a copy of at least a portion of Yahoo’s User Database (UDB), a Yahoo trade secret that contained, among other data, subscriber information including users’ names, recovery email accounts, phone numbers and certain information required to manually create, or “mint,” account authentication web browser “cookies” for more than 500 million Yahoo accounts.

Belan also obtained unauthorized access on behalf of the FSB conspirators to Yahoo’s Account Management Tool (AMT), which was a proprietary means by which Yahoo made and logged changes to user accounts. Belan, Dokuchaev and Sushchin then used the stolen UDB copy and AMT access to locate Yahoo email accounts of interest and to mint cookies for those accounts, enabling the co-conspirators to access at least 6,500 such accounts without authorization.

Some victim accounts were of predictable interest to the FSB, a foreign intelligence and law enforcement service, such as personal accounts belonging to Russian journalists; Russian and U.S. government officials; employees of a prominent Russian cybersecurity company; and numerous employees of other providers whose networks the conspirators sought to exploit. However, other personal accounts belonged to employees of commercial entities, such as a Russian investment banking firm, a French transportation company, U.S. financial services and private equity firms, a Swiss bitcoin wallet and banking firm and a U.S. airline.

During the conspiracy, the FSB officers facilitated Belan’s other criminal activities, by providing him with sensitive FSB law enforcement and intelligence information that would have helped him avoid detection by U.S. and other law enforcement agencies outside Russia, including information regarding FSB investigations of computer hacking and FSB techniques for identifying criminal hackers. Additionally, while working with his FSB conspirators to compromise Yahoo’s network and its users, Belan used his access to steal financial information such as gift card and credit card numbers from webmail accounts; to gain access to more than 30 million accounts whose contacts were then stolen to facilitate a spam campaign; and to earn commissions from fraudulently redirecting a subset of Yahoo’s search engine traffic.

When Dokuchaev and Sushchin learned that a target of interest had accounts at webmail providers other than Yahoo, including through information obtained as part of the Yahoo intrusion, they tasked their co-conspirator, Baratov, a resident of Canada, with obtaining unauthorized access to more than 80 accounts in exchange for commissions. On March 7, the Department of Justice submitted a provisional arrest warrant to Canadian law enforcement authorities, requesting Baratov’s arrest. On March 14, Baratov was arrested in Canada and the matter is now pending with the Canadian authorities.

An indictment is merely an accusation, and a defendant is presumed innocent unless proven guilty in a court of law.

The FBI, led by the San Francisco Field Office, conducted the investigation that resulted in the charges announced today. The case is being prosecuted by the U.S. Department of Justice National Security Division’s Counterintelligence and Export Control Section and the U.S. Attorney’s Office for the Northern District of California, with support from the Justice Department’s Office of International Affairs.

Defendants: At all times relevant to the charges, the Indictment alleges as follows:

Dmitry Aleksandrovich Dokuchaev, 33, was an officer in the FSB Center for Information Security, aka “Center 18.” Dokuchaev was a Russian national and resident.

Igor Anatolyevich Sushchin, 43, was an FSB officer, a superior to Dokuchaev within the FSB, and a Russian national and resident. Sushchin was embedded as a purported employee and Head of Information Security at a Russian investment bank.

Alexsey Alexseyevich Belan, aka “Magg,” 29, was born in Latvia and is a Russian national and resident. U.S. Federal grand juries have indicted Belan twice before, in 2012 and 2013, for computer fraud and abuse, access device fraud and aggravated identity theft involving three U.S.-based e-commerce companies and the FBI placed Belan on its “Cyber Most Wanted” list. Belan is currently the subject of a pending “Red Notice” requesting that Interpol member nations (including Russia) arrest him pending extradition. Belan was also one of two criminal hackers named by President Barack Obama on Dec. 29, 2016, pursuant to Executive Order 13694, as a Specially Designated National subject to sanctions.

Karim Baratov, aka “Kay,” “Karim Taloverov” and “Karim Akehmet Tokbergenov,” 22. He is a Canadian and Kazakh national and a resident of Canada.

Victims: Yahoo; more than 500 million Yahoo accounts for which account information about was stolen by the defendants; more than 30 million Yahoo accounts for which account contents were accessed without authorization to facilitate a spam campaign; and at least 18 additional users at other webmail providers whose accounts were accessed without authorization.

Time Period: As alleged in the Indictment, the conspiracy began at least as early as 2014 and, even though the conspirators lost their access to Yahoo’s networks in September 2016, they continued to utilize information stolen from the intrusion up to and including at least December 2016.


Crimes:

Count(s) Defendant(s) Charge Statute                 18 U.S.C. Conduct Maximum Penalty
1 All Conspiring to commit computer fraud and abuse § 1030(b) Defendants conspired to hack into the computers of Yahoo and accounts maintained by Yahoo, Google and other providers to steal information from them.


First, Belan gained access to Yahoo’s servers and stole information that allowed him, Dokuchaev, and Sushchin to gain unauthorized access to individual Yahoo user accounts.

Then, Dokuchaev and Sushchin tasked Baratov with gaining access to individual user accounts at Google and other Providers (but not Yahoo) and paid Baratov for providing them with the account passwords. In some instances, Dokuchaev and Sushchin tasked Baratov with targeting accounts that they learned of through access to Yahoo’s UDB and AMT (e.g., Gmail accounts that served as a Yahoo user’s secondary account).

10 years
2 Dokuchaev

Sushchin

Belan

Conspiring to engage in economic espionage § 1831(a)(5) Starting on Nov. 4, 2014, Belan stole, and the defendants thereafter transferred, received and possessed the following Yahoo trade secrets:

  • the Yahoo UDB, which was proprietary and confidential Yahoo technology and information, including subscriber names, secondary accounts, phone numbers, challenge questions and answers;
  • the AMT, Yahoo’s interface to the UDB; and
  • Yahoo’s cookie “minting” source code, which enabled the defendants to manufacture account cookies to then gain access to individual Yahoo user accounts.
15 years
3 Dokuchaev

Sushchin

Belan

Conspiring to engage in theft of trade secrets § 1832(a)(5) See Count 2 10 years
4-6 Dokuchaev

Sushchin

Belan

Economic espionage §§ 1831(a)(1), (a)(4), and 2 See Count 2 15 years (each count)
7-9 Dokuchaev

Sushchin

Belan

Theft of trade secrets §§ 1832(a)(1), and 2 See Count 2 10 years (each count)
10 Dokuchaev

Sushchin

Belan

Conspiring to commit wire fraud § 1349 The defendants fraudulently schemed to gain unauthorized access to Yahoo’s network through compromised Yahoo employee accounts and then used the Yahoo trade secrets to gain unauthorized access to valuable non-public information in individual Yahoo user accounts. 20 years
11-13 Dokuchaev

Sushchin

Belan

Accessing (or attempting to access) a computer without authorization to obtain information for the purpose of commercial advantage and private financial gain. §§ 1030(a)(2)(C), 1030(c)(2)(B)(i)-(iii), and 2 The defendants gained unauthorized access to Yahoo’s corporate network and obtained information regarding Yahoo’s network architecture and the UDB. 5 years

(each count)

14-17 Dokuchaev

Sushchin

Belan

Transmitting code with the intent to cause damage to computers. §§ 1030(a)(5)(A), 1030(c)(4)(B), and 2 During the course of their unauthorized access to Yahoo’s network, the defendants transmitted code on Yahoo’s network in order to maintain a persistent presence, to redirect Yahoo search engine users and to mint cookies for individual Yahoo accounts. 10 years (each count)
18-24 Dokuchaev

Sushchin

Belan

Accessing (or attempting to access) a computer without authorization to obtain information for the purpose of commercial advantage and private financial gain. §§ 1030(a)(2)(C), 1030(c)(2)(B)(i)-(iii), and 2 Defendants obtained unauthorized access to individual Yahoo user accounts. 5 years

(each count)

25-36 Dokuchaev

Sushchin

Belan

Counterfeit access device fraud §§ 1029(a)(1), 1029(b)(1), and 2 Defendants used minted cookies to gain unauthorized access to individual Yahoo user accounts. 10 years (each count)
37 Dokuchaev

Sushchin

Belan

Counterfeit access device making equipment §§ 1029(a)(4) Defendants used software to mint cookies for unauthorized access to individual Yahoo user accounts. 15 years
38 Dokuchaev

Sushchin

Baratov

Conspiring to commit access device fraud §§ 1029(b)(2) Defendants Dokuchaev and Sushchin tasked Baratov with gaining unauthorized access to individual user accounts at Google and other Providers and then paid Baratov for providing them with the account passwords. In some instances, Dokuchaev and Sushchin tasked Baratov with targeting accounts that they learned of through access to Yahoo’s UDB and AMT (e.g., Gmail accounts that served as a Yahoo user’s secondary account). 7 ½ years.
39 Dokuchaev

Sushchin

Baratov

Conspiring to commit wire fraud § 1349 See Count 38 20 years
40-47 Dokuchaev

Baratov

Aggravated identity theft § 1028A(a)(1) See Count 38 2 years

bookmark_borderRadical Christian Terrorists and the Zombie Apocalypse

EARTH — Imagine a group of radical Christians taking over the government and trying to bring on the Rapture (aka The Apocalypse) and the Second Coming.

You no longer need to imagine. A conspiracy of Evangelical Christians are trying to facilitate The End Of Times. They want to fulfill biblical prophecies including:

  1. The Revival of the Roman Empire
  2. The Emergence of the Antichrist
  3. The Covenant with Israel
  4. Three Periods Between the Rapture and the Second Coming
  5. The War with Russia
  6. The Great Tribulation: Armageddon

The Radical Christian Terrorists believe they will be “saved” when these events occur.

ESCHATOLOGY
Eschatology is the part of theology concerned with death, judgment, and the final destiny of the soul and of humankind.

THE RAPTURE / ZOMBIE APOCALYPSE
Daniel 12
The Time of the End

2 Many of those who are dead in the ground will awake, these to everlasting life, but the others to disgrace and everlasting contempt.

Thessalonians 4:17
17 Then we who are alive and remain will be caught up together with them in the clouds to meet the Lord in the air, and so we shall always be with the Lord.

In Christian eschatology, the Rapture refers to the prophesied event when “Christian believers who have died will be raised and believers who are still alive and remain shall be caught up together with them (the resurrected dead believers) in the clouds to meet the Lord Jesus Christ in the air.”

APOCALYPSE
The apocalypse is the complete and final destruction of the world as prophesied in the biblical books of Daniel and Revelation (the last book of the Bible.)

The Four Horsemen of the Apocalypse in the book of Revelation are horsemen on white, red, black, and pale horses. The riders are often seen as symbolizing:

  1. Conquest, Pestilence, the Christ or the Antichrist
  2. War
  3. Famine
  4. Death

“The Christian apocalyptic vision is that the four horsemen are to set a divine apocalypse upon the world as harbingers of the Last Judgment.”

Revelation 6:7-8
When the Lamb broke the fourth seal, I heard the voice of the fourth living creature saying, “Come.” I looked, and behold, an ashen (pale) horse; and he who sat on it had the name Death; and Hades was following with him. Authority was given to them over a fourth of the earth, to kill with sword and with famine and with pestilence and by the wild beasts of the earth.

  • The first seal is broken and the first of the four living creatures introduces a white horse whose crowned rider, equipped with a bow, goes out to conquer.
  • The second seal is broken and the second of the four living creatures introduces a red horse, whose rider wields a great sword.
  • The third seal is broken and the third of the four living creatures introduces a black horse, whose rider carries a pair of scales, goes out.
  • The fourth seal is broken and the fourth of the four living creatures introduces an ashen horse comes out, whose rider has the name Death and Hades follows him.
  • The fifth seal is broken revealing the souls of those who had been slain for the “Word of God”.
  • The sixth seal is broken “and there was a great earthquake; and the sun became black as sackcloth made of hair, and the whole moon became like blood; and the stars of the sky fell to the earth, The sky was split apart, every mountain and island were moved out of their places.”
  • Mankind hides themselves in the caves and mountains acknowledging the presence of Him who sits on the throne and the wrath of the Lamb.

bookmark_borderFormer Employees Sue Microsoft For PTSD

By Daniel Brouse for The Membrane Domain Cybersecurity

Two former Microsoft employees have filed a lawsuit against Microsoft claiming PTSD. Their job as part of the security team was to review users content that had been flagged by automated software. For instance, pictures sent through Hotmail or other Microsoft services that appeared suspicious were then reviewed by humans.

The two ex-employees, Henry Soto and Greg Blauert, jobs were to uphold Microsoft’s legal obligation to inform authorities of illegal images. Mr. Soto’s and Mr. Blauert’s primary responsibility was to report pictures of child abuse to the US National Center for Missing and Exploited Children.

Mr. Soto viewed “many thousands of photographs and videos of the most horrible, inhumane and disgusting content one can imagine,” the lawsuit stated. “Many people simply cannot imagine what Mr. Soto had to view on a daily basis as most people do not understand how horrible and inhumane the worst people in the world can be.”

Microsoft disputed the claims. “Microsoft takes seriously its responsibility to remove and report imagery of child sexual exploitation and abuse being shared on its services, as well as the health and resiliency of the employees who do this important work.”

bookmark_borderTrump Security Breach

For months, the security community has known that both the DNC and GOP were hacked. The DNC hack was used to undermine Hillary. The GOP / Trump hacks were meant for blackmailing Trump. No surprises here.

U.S. security agencies were aware of Donald Trump’s security breaches since last summer. The information was in the public domain by August of 2016. The Donald was given a copy of the report long before the story appeared in the New York Times.

In a hearing before the Senate Select Committee on Intelligence, FBI director James Comey said attackers penetrated GOP organizations and stole Republican National Committee emails. “There was evidence that there was hacking directed at state-level organizations and the RNC…. Information was harvested from there, but it was old stuff. None of that was released”, Comey said.

Back in August of 2016 digital security firm ThreatConnect said, “We believe DC Leaks is another Russian-backed influence outlet.” DC Leaks had released 300 stolen emails from Republican targets including the staffs of Sen. John McCain, Lindsey Graham, Michele Bachmann and party officials in several states.

In October of 2016, Richard Andres, a cybersecurity and national security strategy expert with the U.S. military’s National War College said, “What we’ve been seeing here in the U.S. so far is mild by comparison to what they do in their own backyard. If they continue to escalate, we should expect to increasingly see false flag operations designed to implicate various political actors, falsified leaks, blackmail, false calls to their opponents’ political supporters and more

The Russians have gained accessed to the DNC and GOP mainly through “spearphishing.” Spearphishing is when a hacker gets someone to click on an email, attachment, link or photo. Malware is then installed on the victim’s computer that allows hackers to exploit the network. “Essentially people are opening their front door and letting them in,” said Toni Gidwani, a former Defense Intelligence Agency official whose ThreatConnect cybersecurity firm has investigated many of the hacks. “It’s something they keep coming back to because it works.”

It is not a matter of politics. It is a matter of national security. All sides need people to go to jail over the security breaches — Republicans, Democrats and Russians.

On January 11, Donald Trump tried to skirt the issue during a press conference and said he didn’t have any business in Russia. These statements were very misleading, if not an out-an-out lie. Donald Trump has substantial investment from Russians for businesses in other countries. After Trump went bankrupt 6 times, he was unable to readily borrow money from any reputable institution. Instead, he took money from Russian oligarchs and Russian mobs.

In 2008, Donald Trump Jr. attended a real estate conference and stated, “Russians make up a pretty disproportionate cross-section of a lot of our assets. We see a lot of money pouring in from Russia.”

Bayrock is a Russian backed business that has been implicated in money laundering. The Financial Times reported, “The Republican presidential nominee and Bayrock were both based in Trump Tower and they joined forces to pursue deals around the world — from New York, Florida, Arizona and Colorado in the US to Turkey, Poland, Russia and Ukraine. Their best-known collaboration — Trump SoHo, a 46-storey hotel-condominium completed in 2010 — was featured in Mr Trump’s NBC television show The Apprentice.”

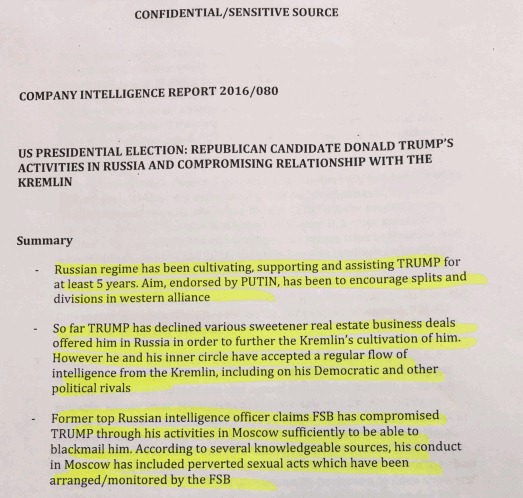
THE REPORT:
Trump Intelligence Allegations

Trump Intelligence Allegations

MORE

Russia Attempts to Hack Electric Grid
Malware associated with a Russian hacking operation, Grizzly Steppe, was found on a Burlington Electric computer. It appears as though Russia was trying to access the power grid; however, the infected computer was not connected to the network. “Vermonters and all Americans should be both alarmed and outraged that one of […]

Russia And Cybersecurity
Cozy Bear and Fancy Bear are two hacking organizations from Russia. Cozy Bear (classified as advanced persistent threat APT29) are believed to be associated with Russian intelligence. Fancy Bear (also known as APT28, Pawn Storm, Sofacy Group, Sednit and STRONTIUM) is a cyber espionage group believed to be sponsored by the […]

bookmark_borderGay Church Vs. Corruption

WEST CHESTER, PA — A microcosm of what is going on globally can be found at the corner’s of Gay and Church Street in West Chester, Pennsylvania. It is the County Seat and has a university within the Borough — a collision of humanity and hypocrisy.  Musicians, and artists of a wide variety, often come together at the corners of Gay and Church. Though the name Gay Church Band was meant as a location not a political statement, it is ironic that art and spirit are under attack at the corner. Police brutality in conspiracy with bureaucracy is unfortunately a reality.

REFERENCES:

Hate Crimes, Human and Civil Rights Violations in West Chester, Pennsylvania

West Chester Restricts Singing & Dancing (October 18, 2016)

Video Sample Of Gay Church Bashing

Gay Church Picture Collage

bookmark_borderCyber Security Landscape

Q: Is it true that flashlight apps for your smartphone may contain malware?
A: It’s not just flashlight apps. Over 90% of freeware (free computer software for photos, converting Youtube videos, etc.) and free app downloads contain malware that is secretly added to your device. Besides stealing your data, they can corrupt files or worse. Quite often they use your connection and device to attack other people making it look like you are the bad guy. Attacks on the Whitehouse, FBI, CIA and military bases (such as Andrews Air Force Base) have happened this way. As far as smartphone apps go, there are not that many legit apps. Apple is of particular concern because their developer’s “tool kit” has been compromised. The result was many legit app developers used the official Apple tool kit, but ended up incorporating malware. This is what happened with most of the flashlight apps. (1)

By the way, the apps developed for Facebook are often used to compromise your Facebook account and steal your identity, as well as, attack all your friends. If Facebook doesn’t make the app, don’t use it. Examples of bogus apps include “What song was a hit on your birthday?”, “How loyal are you?”, “Who is stalking you?”, “Which season of the year are you?”, “3 reasons to love yourself!”, “Let’s make a drawing of you” and “Yourself as an oil painting”.

Q: How do I know if Facebook makes the app?
A: If Facebook makes the app, it is usually automatically integrated into the interface. Examples include when Facebook added more choices to the “like” button and the app they put in your feed about “1 year ago today”. Those are Facebook apps. The ones that tell you about your loyalty, stalkers, hit record on your birthday, compare you to your friends, etc. are clickbait and should be avoided. Almost all of these apps abuse your friends. Some of them allow your account to do criminal activity, such as, post sunglasses or shoes for sale tagging your friends without your knowledge. Some of them do even worse stuff, such as, compromise your account and use your account to surreptitiously to do a host of bad activities.

Q: Are Android apps safer than Apple apps?
A: Most apps are not developed by Google, Microsoft or Apple. If someone is giving an app away, it is probably for ill purposes. Nevertheless, the advantage of Android — it is built on Linux (open source code.) This means anyone can see the source and/or fix the computer code. That is not the case with Apple or Microsoft. We suggest Android on your phones and Linux on your computers.

Q: My tech-savvy son says it is safe to download apps from Google. Is the Google app store safe?
A: it’s not Google… it is the open source community. Google doesn’t own Android. Android is based on Linux (free open source software) the Linux community is serious about security. We’ve been involved with Linux development since the 1990’s. Apple and Microsoft are based on proprietary software which is the opposite of the open source philosophy. In any event, none of us like Google for other reasons; however, their exploitation of Linux is better for mankind than Apple and Microsoft. Google Android apps are a better bet than other OS’s (operating systems) because they use Linux. That doesn’t mean you should trust Google. Do not trust Google.

Q: What about GPS apps?
A: GPS apps are the most exploited function/app of a smartphone. Not only do private companies exploit the data but bad guys and our government do, too. So my advice is what I did for my Dad. He suffers from dementia and tends to wonder off. We got a Metro PCS smartphone and the sole use is for tracking my Dad with a GPS app. If you want a GPS, use a separate device.

An example of a GPS smartphone app scam recently happened in Chester County, PA. Bad guys hacked GPS apps and sent fraudulent email traffic tickets to unsuspecting motorists. (2)

References:
1) Apple’s App Store infected with XcodeGhost malware in China after major security breach. China’s “Great Firewall” may have been partly to blame for the first major attack on Apple Inc’s (AAPL.O) App Store, but experts also point the finger at lax security procedures of some big-name Chinese tech firms and how Apple itself supports developers in its second biggest market. A malicious program, dubbed XcodeGhost, hit hundreds – possibly thousands – of Apple iOS apps, including products from some of China’s most successful tech companies used by hundreds of millions of people. (Reuters)

2) “Beware This Crazy Speeding Ticket Scam” Philadelphia-area residents have been targeted, and the level of information the perpetrator has is downright scary. The Tredyffrin Police Department in Chester County announced the speeding ticket scam this week, explaining that three local residents reported receiving emails notifying them of speeding infractions. Tredyffrin doesn’t have speed cameras, and the police say that they have nothing to do with these citation notices, but here’s the thing: The residents were, in fact, speeding at the locations cited in the citations. How is this possible? Well, investigators suspect that a hacker has exploited a security flaw in some GPS-enabled smartphone apps. (Philly Magazine)

More Internet Security

bookmark_borderWar Declared

Washington DC — On September 10, 2014 between 9PM and 9:15PM, President Obama declared war on the Islamic State (ISIS).

“Our objective is clear: We will degrade, and ultimately destroy, ISIL through a comprehensive and sustained counter-terrorism strategy.”

Critics raised debate on the irony of Obama going into Iraq after his position on getting out of Iraq.

President Obama Declaring War on ISIL